Jia Lissa
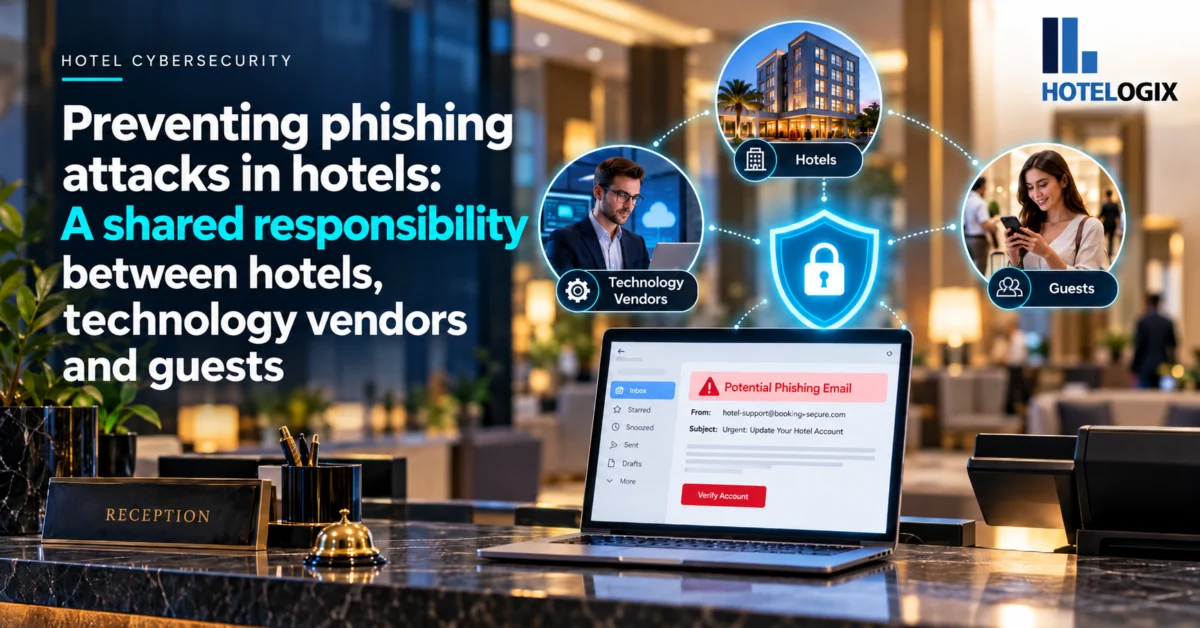
For decades, the banking and financial services sector has served as the primary battleground for sophisticated phishing operations. Criminals have long perfected the art of impersonating institutions to harvest credentials, hijack accounts, and orchestrate fraudulent transfers. However, a seismic shift has occurred in the threat landscape. Cybercriminals have pivoted their "playbook" toward the global hospitality and travel industry, viewing hotels as the new, high-value frontier for data theft and financial extortion.
As of May 2026, the hospitality sector is witnessing a harrowing surge in digital threats. According to data from Check Point, the industry faced an average of 2,291 cyberattacks per organization during that month alone—a staggering 24% increase compared to the same period in 2025. This escalation is not merely a byproduct of increased digital usage; it is a calculated exploitation of the industry’s most vulnerable asset: human trust.
The Goldmine: Why Hotels Are Prime Targets
To understand the surge, one must look at the data hotels process daily. A single hotel property acts as a clearinghouse for highly sensitive information: guest names, contact details, granular booking histories, payment card data, government-issued identity documents, and intimate communication threads.
For a cybercriminal, this is a "goldmine." Unlike a one-off retail transaction, a hotel stay involves a multi-stage data relationship. Once an attacker gains a foothold, they don’t just secure a credit card number; they secure a roadmap of a guest’s life—their movements, their associations, and their financial habits. This density of PII (Personally Identifiable Information) makes the hospitality sector an irresistible target for organized crime syndicates seeking rapid monetization.
Chronology of a Digital Siege: Recent Campaigns
The methods employed by these threat actors have evolved from crude "Nigerian Prince" style emails to hyper-sophisticated, multi-stage malware campaigns.
The Rise of "ClickFix" and Remote Access Trojans
In late 2024 and early 2025, Microsoft Threat Intelligence identified a worrying trend: the "ClickFix" campaign. Attackers began impersonating major platforms like Booking.com, targeting front-desk and reservations staff. These emails are designed to induce panic, claiming a guest has had a "serious issue" and requires immediate intervention.
When staff click the malicious link, they are often redirected to a fake portal that triggers a "Blue Screen of Death" (BSOD) or a system error. The "fix" for this fake error requires the user to execute specific PowerShell commands. Unbeknownst to the employee, these commands install remote-access trojans (RATs) like DCRat or VenomRAT, granting the attacker total control over the hotel’s reservation systems.
The Calendly Exploitation
By mid-2026, the tactics grew even more insidious. Attackers began leveraging trusted platforms like Calendly to bypass email authentication filters. Because Calendly is a legitimate, widely used service, its automated emails often pass through SPF, DKIM, and DMARC security checks unscathed. By embedding malicious links within these "trusted" calendar invites, hackers successfully deployed backdoors into European and Asian hotel networks, allowing for long-term, persistent access to internal data repositories.
Notable Breaches
The reality of these threats was punctuated in May 2026, when BWH Hotels (Best Western, WorldHotels, and SureHotels) confirmed a significant web-app breach. Attackers held access to reservation data for six months, compromising guest contact details and stay records. This stolen data is now being cycled back into the ecosystem to fuel "spear-phishing" campaigns—highly personalized attacks that are significantly harder for staff to identify as fraudulent.
The Psychology of the Attack: Weaponizing Empathy
Successful phishing is rarely a numbers game; it is a psychological operation. Attackers conduct deep reconnaissance on hotel workflows, identifying who handles finance, who manages guest complaints, and who coordinates with third-party vendors.
They weaponize human emotions, specifically:
- Urgency: "Your account will be suspended in 24 hours."
- Fear: "I am reporting your hotel for a poor experience."
- Curiosity: "Check out these photos from my stay last week."
- Authority: "This is a mandatory update from your OTA partner."
When an employee at a busy front desk receives an email from a "guest" complaining about a bad stay with attached "evidence" (a ZIP file), the pressure to resolve the issue before a negative review is posted often overrides standard cybersecurity protocol. The employee opens the attachment, and the breach is complete.
Implications: The Cost of Lost Trust
The consequences of these breaches extend far beyond the initial IT remediation costs. According to IBM’s Cost of a Data Breach Report 2025, the average cost of a data breach in the hospitality industry reached $4.03 million between March 2024 and February 2025.
The Triple-Threat Impact:
- Financial Erosion: Beyond direct theft, hotels face massive regulatory fines (GDPR, CCPA, etc.) and the cost of forensic investigations and legal fees.
- Brand Degradation: Trust is the primary currency of the hospitality industry. A data breach involving guest passports or payment records can cause irreparable damage to a brand’s reputation, leading to long-term booking declines.
- Operational Paralysis: As seen in recent ransomware incidents, a compromised PMS (Property Management System) can force a hotel to revert to manual, pen-and-paper operations, effectively crippling revenue generation during the restoration period.
A Blueprint for Defense: Adopting the "Banker’s Mindset"
If hotels are being treated like banks by attackers, they must begin to defend themselves like banks. This requires a fundamental shift in security culture.
1. Hardening the Tech Stack
Hotels must move beyond basic firewalls. This includes:
- Email Security Gateways: Implementing robust protocols that go beyond standard SPF/DKIM to include AI-driven threat detection that analyzes behavioral anomalies.
- Zero-Trust Access: Ensuring that employees have access only to the specific data required for their role. A front-desk clerk should not have administrative access to the entire PMS database.
- Framework Compliance: Aligning operations with established standards such as NIST (USA), Cyber Essentials (UK), and PCI DSS to ensure a baseline of resilience.
2. Radical Staff Education
Cyber-awareness training cannot be an annual, check-the-box event. It must be continuous. Staff must be trained to treat any unsolicited request—even those appearing to come from known OTAs—with extreme skepticism. "Verify, then Act" should be the industry mantra. If an email seems suspicious, a quick, independent phone call to the alleged sender can prevent a million-dollar disaster.
3. Protecting the Guest Journey
The guest, too, is a target. Hotels must clearly communicate their official channels of communication. Guests should be explicitly warned never to download apps or click payment links received via unverified emails. By providing a secure, centralized portal for all guest interactions, hotels can minimize the "attack surface" where hackers usually lurk.
The Responsibility of Technology Partners
The burden of security does not rest solely on the shoulders of the hotelier. Property Management System (PMS) providers and third-party vendors are critical nodes in the security chain. These providers must treat every API integration, webhook, and login portal as a potential point of entry for malicious actors.
Technology partners have a moral and contractual obligation to provide more than just software; they must provide "secure-by-design" infrastructure. This means proactive threat hunting, regular penetration testing, and transparent communication regarding vulnerabilities.
Conclusion: The Path Forward
The digital age has brought unprecedented convenience to the travel experience, but it has also opened the door to a new era of criminality. As long as hotels continue to process high-value data, they will remain in the crosshairs of global cyber syndicates.
Phishing is no longer just a "tech problem"—it is a business survival issue. By acknowledging the reality of these threats, investing in human-centric security training, and building resilient, zero-trust technological ecosystems, the hospitality industry can transform from a target into a fortress. Protecting the guest experience today means securing the data that makes that experience possible. In the modern era, the most vital amenity a hotel can offer is not a luxury room or a gourmet meal, but the ironclad security of their guests’ information.

 Evan Lee Salim
 Iffa Jayyana