Asro
The arrest of a 24-year-old Dutch national has sent shockwaves through the global cybersecurity landscape, peeling back the layers of a complex, dual-life narrative that has captivated law enforcement and intelligence agencies worldwide. Pepijn van der Stap, once a respected software engineer and security researcher, now sits at the center of a sprawling international investigation into the prolific and aggressive hacking collective known as "ShinyHunters."
His detention, which occurred on or around September 16, 2026, was not merely a routine police action; it served as a catalyst for a chaotic and dangerous escalation in cyber-attacks, targeting some of the world’s most secure institutions, including the United States Federal Bureau of Investigation (FBI).
The Double Life of "Umbreon"
For those who knew him professionally, van der Stap was a diligent, albeit troubled, contributor to the cybersecurity ecosystem. By day, he worked as an offensive security lead at the Amsterdam-based firm Neo Security and previously contributed his expertise to the Dutch Institute for Vulnerability Disclosure (DIVD). Yet, in the shadows of the internet, he operated under the alias "Umbreon"—a moniker derived from the Pokémon franchise that became synonymous with high-stakes data theft and extortion.
Van der Stap’s criminal career was marked by a chilling "Dr. Jekyll and Mr. Hyde" duality. During his 2023 trial, where he faced charges related to millions of euros in illicit gains, he admitted to his role in leaking sensitive databases on dark-web forums like RaidForums and Breached. Despite his public persona as a reformed hacker striving for redemption, internal investigations suggest that the pull of his digital obsession—collecting and organizing stolen data—remained a dominant force in his life.
A Chronology of Escalation
The timeline of events surrounding van der Stap’s arrest reveals a desperate attempt by the remaining members of ShinyHunters to assert dominance and shield their operations from scrutiny.

- February 2026: ShinyHunters executes a devastating social engineering attack on Odido, the Netherlands’ largest telecommunications provider. Using a native Dutch-speaking operative, the group bypassed security protocols to exfiltrate the personal data of over 6.2 million Dutch citizens.
- September 9, 2026: In a final interview with KrebsOnSecurity, van der Stap expresses a desire to move past his criminal history, claiming to be fully committed to his work in offensive security.
- September 16, 2026: Dutch authorities apprehend van der Stap. Reports from witnesses suggest a significant seizure of digital equipment from his residence.
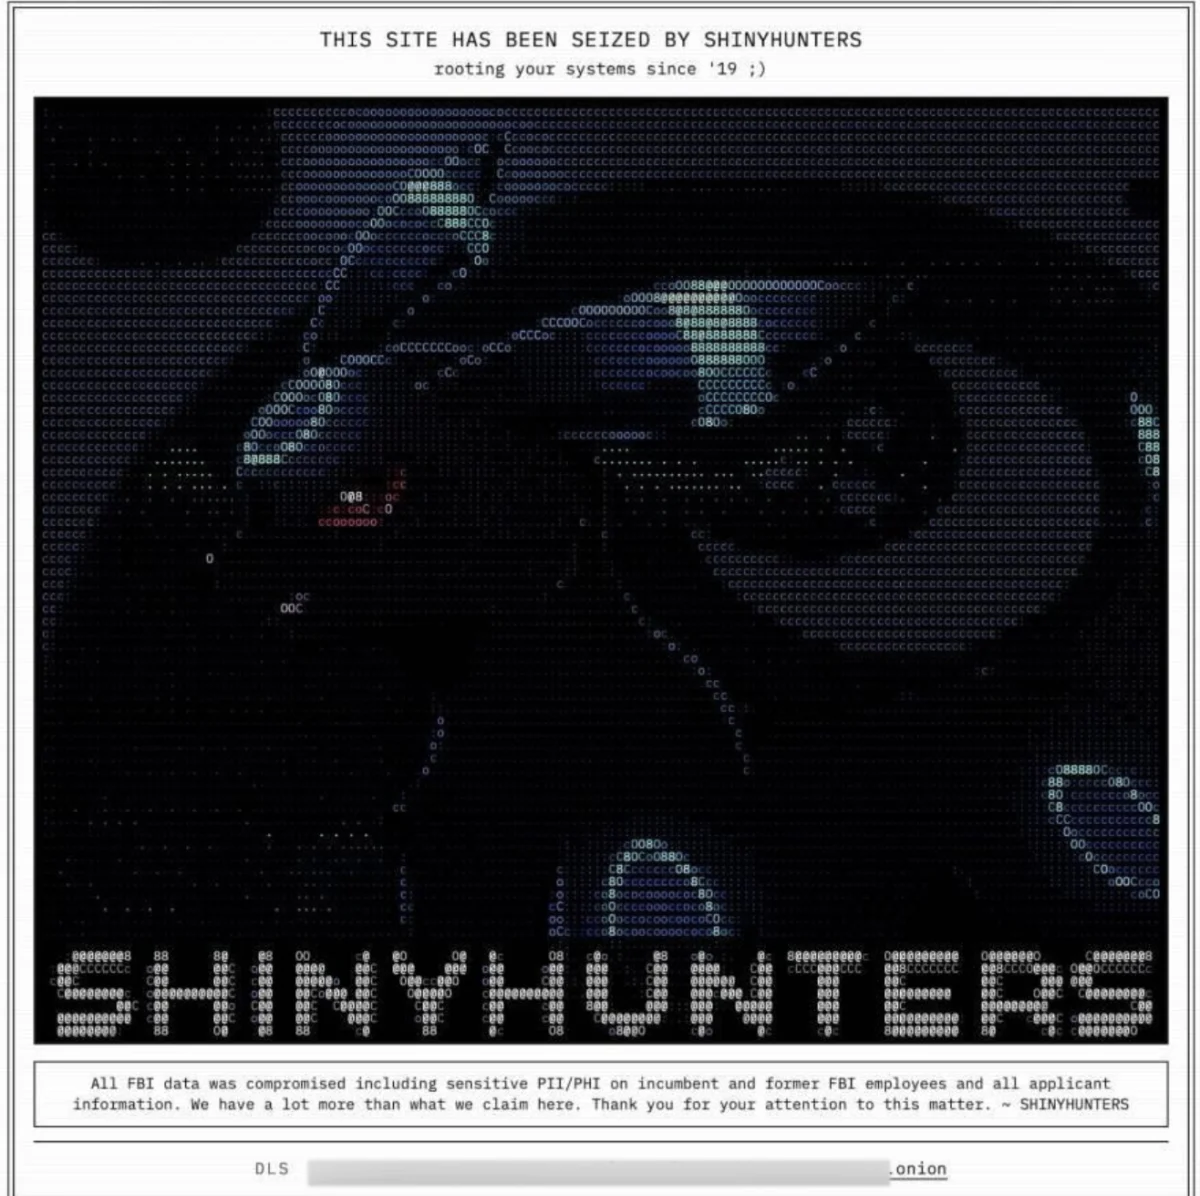
- September 18–22, 2026: In the immediate wake of the arrest, ShinyHunters launches a series of brazen attacks. The group claims responsibility for breaching the FBI’s job application portal (apply.fbijobs.gov), leaking Social Security numbers and psychiatric files of federal employees.
- September 29, 2026: Dutch news outlet RTL reports that the investigation into van der Stap has taken a dark turn, with authorities now suspecting him of orchestrating at least two murder-for-hire plots abroad.
Anatomy of the FBI Breach: A Zero-Day Weaponized
The breach of the FBI’s infrastructure was not a random act of digital vandalism; it was a tactical operation that utilized a critical vulnerability in Oracle’s PeopleSoft software (CVE-2026-35273). This software, a standard for human resources and payroll management across major global corporations, became the primary vector for ShinyHunters’ recent campaign.
Security experts at Mandiant and the Google Threat Intelligence Group (GTIG) confirmed that the group successfully mass-exploited this flaw to infiltrate industries ranging from healthcare and transportation to government agencies. Even after security teams deployed web application firewall (WAF) rules to mitigate the threat, ShinyHunters utilized sophisticated URL-encoding techniques to bypass these defenses, proving their advanced capabilities.
The "Umbreon" connection remained a glaring feature of these attacks. The defacement image left on the FBI’s portal featured the same ASCII art of the Pokémon Umbreon that van der Stap had used in previous operations. However, intelligence sources suggest this may have been a calculated move by a rival within the group—a teenage hacker known as "Rey"—to frame van der Stap and consolidate power within the collective.
The Rise of "Rey" and the SLSH Coalition
The transition of power within the hacking world is rarely peaceful. Sources close to the investigation describe a significant shift in the operational philosophy of ShinyHunters under the leadership of "Rey," a Jordanian teenager associated with the "ScatteredLapsussHunters" (SLSH) coalition.
SLSH represents a dangerous merger of three distinct hacking cultures: Scattered Spider, LAPSUS$, and ShinyHunters. Unlike the more methodical approach of previous generations, Rey’s leadership is characterized by "performative" hacking. His use of taunting memes on social media, mocking the FBI and the Russian ransomware group Cl0p, indicates a desire for infamy that distinguishes him from the more data-focused approach of van der Stap.

The tension between these factions likely stemmed from the failed partnership with the supply-chain hacking group "TeamPCP." After ShinyHunters allegedly cut TeamPCP out of a lucrative deal involving stolen credentials, the resulting fallout and subsequent arrests in Australia created a power vacuum that Rey moved to fill.
Official Responses and Implications
The Dutch authorities have remained largely tight-lipped regarding the specifics of the ongoing investigation, though their resolve is clear. In a statement released following the arrest, the Dutch police emphasized that the suspect would face the Rotterdam District Court, signaling a move toward full prosecution.
The FBI has also broken its silence, with Brett Leatherman, assistant director of the bureau’s cyber division, issuing a stern warning to the remaining members of the collective. "Arrests have a way of changing who is willing to talk," Leatherman stated, urging the hackers to surrender before their digital footprints lead federal agents directly to their doorsteps.
The Broader Impact on Cybersecurity
The implications of the ShinyHunters saga extend far beyond the legal fate of Pepijn van der Stap. The incident underscores a critical vulnerability in global supply chains: the reliance on centralized, third-party software like Oracle’s PeopleSoft. As these platforms become the primary targets for mass-scale exploitation, organizations are being forced to rethink their security posture, moving away from passive firewalls toward more robust, zero-trust architectures.
Furthermore, the involvement of AI-assisted attacks and the rise of decentralized, teenage-led hacking syndicates pose a challenge that traditional law enforcement is still learning to navigate. The shift from "collectors" like van der Stap—who were driven by a compulsion to organize and hoard data—to "extortionists" like Rey, who are motivated by chaos and branding, marks a dangerous evolution in the cybercrime threat landscape.

As the case continues to unfold, the global security community remains on high alert. The "ShinyHunters" collective has proven that even when individual members are removed from the board, the underlying infrastructure and the motivation to monetize stolen sensitive information remain. Whether this marks the beginning of the end for the group or merely the start of a more reckless phase of operations remains to be seen.
For now, the story of Pepijn van der Stap serves as a sobering reminder of the thin line between digital expertise and criminal liability, and the profound, often tragic, consequences of choosing the latter.

 Ali Ikhwan
 Sagoh