
 Rifan Muazin
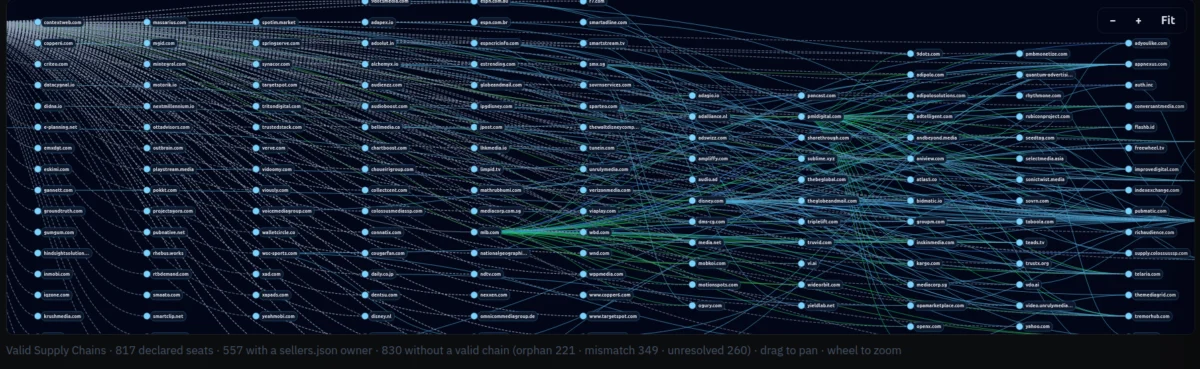
For the average internet user, the digital advertising ecosystem is a black box. We visit a news site, browse a retailer, or open a mobile game, and within milliseconds, a complex auction occurs behind the scenes. Dozens of entities bid for the right to serve an ad, harvest our location data, and build a psychological profile of our habits. Until now, this process has remained largely opaque, walled off by the complexity of programmatic advertising and the proprietary interests of massive data brokers.
A new, free service called DecryptAds is changing that paradigm. By scraping, correlating, and visualizing the "hidden" files that websites and apps are required to publish, DecryptAds provides a transparent map of the entities tracking us. For security professionals, privacy advocates, and concerned consumers, this tool offers a long-overdue look at the supply chain of modern digital surveillance.
The Infrastructure of Transparency: How It Works
The internet functions on a series of semi-public disclosure files that many users—and even many IT professionals—rarely examine. DecryptAds acts as a specialized search engine for these critical documents:
- ads.txt: A file hosted on a domain that lists authorized digital sellers and data brokers.
- app-ads.txt: The mobile and smart-TV equivalent, documenting who is permitted to harvest data or serve ads within an application.
- buyers.json/sellers.json: Structured data identifying the entities buying, selling, or reselling ad inventory.
Zach Edwards, Chief Research Officer for DecryptAds and a threat researcher at Infoblox, explains that while this data has technically been "public," it has remained effectively inaccessible. "It’s an adtech tool, but we’re approaching it from a security perspective," Edwards notes. "It’s built for privacy and security use cases that have been historically underserved."

By cross-referencing these files, DecryptAds can identify patterns that a single file could never reveal. It uncovers cloned declarations across unrelated domains, suspicious seller removals, and supply paths that appear in bid logs but never in a publisher’s authorized-seller list.
Chronology: From Adtech Obscurity to Public Scrutiny
The push for transparency in digital advertising has gained momentum in recent years, driven by both regulatory pressure and a surge in cyber threats.
- 2017-2020: The introduction of the
ads.txtstandard by the Interactive Advertising Bureau (IAB) was intended to prevent domain spoofing and ad fraud. However, it inadvertently created a directory of every entity a publisher does business with, turning a security feature into a roadmap for data brokers. - 2022-2025: Several U.S. states—including California, Oregon, Texas, and Vermont—passed legislation requiring data brokers to register if they handle consumer data. This forced a new level of disclosure that DecryptAds has successfully ingested.
- 2026 (August): The official launch of DecryptAds.com marks a turning point, moving these disclosures from static, unreadable text files into a searchable, analytical database.
- Present: Researchers are now using this platform to link disparate "slop" websites (AI-generated content farms) to sophisticated malicious ad networks, providing evidence for regulators and cybersecurity analysts.
Supporting Data: The Case of ESPN and Beyond
To understand the scale of the surveillance, one need only look at a mainstream giant like espn.com. A search on DecryptAds reveals 143 ad partners and 19 registered data broker domains. Of those brokers, nearly 50% are collecting geolocation data from visitors who have not enabled ad blockers. Three others explicitly disclose that they are collecting device fingerprints and sensitive personal information.
The implications for national security are equally stark. DecryptAds highlights "geo-risk" partners, flagging companies based in Russia, China, or jurisdictions with close financial ties to these nations, such as Cyprus and the United Arab Emirates (UAE).

The platform’s dossier on Between Digital serves as a chilling case study. While the firm lists a New York address, DecryptAds flags it as a Russian-operated entity, noting that its publisher payments are processed through Alfa Bank—a Russian financial institution under heavy U.S. sanctions. Despite these red flags, an investigation shows that Between Digital is active on major U.S. military-focused news outlets, including Army Times, Air Force Times, and Defense News.
The "Quiet Removal" Phenomenon
One of the most innovative features of the platform is the "Quiet Removals Feed." In the current adtech industry, when a network discovers an advertiser is spreading malware or engaging in fraudulent activity, they often remove the offender from their sellers.json file without notifying the public or other industry partners.
"The ban is just removing them from the file, but they told nobody," Edwards explains. "One day it was there, the next it was gone." By tracking these changes in real-time, DecryptAds allows security teams to identify "dodgy" firms that have been quietly blacklisted by major exchanges, providing a vital signal in the fight against supply-chain attacks.
Implications: Malvertising and the AI "Slop" Crisis
The rise of AI-generated "slop" websites has created a perfect environment for malvertising. Because these content farms prioritize volume over reputation, they often sign up with the lowest-tier, high-risk ad networks.

"None of these slop AI content farms are paying for protection," Edwards warns. "It becomes a greased rail to target users with malicious ads."
The threat is compounded by the lack of transparency regarding the "Supply Chain Object" (SCO). The SCO is a piece of data attached to an ad bid that reveals every intermediary between the publisher and the final buyer. Currently, major ad networks do not share this data externally. Without the SCO, victims of a "zero-click" malware payload are often left unable to trace the source of the attack. DecryptAds is positioning itself as a catalyst to pressure the industry into making this data available, arguing that true accountability is impossible without it.
Taking Control: A Practical Guide for Users
The findings from DecryptAds underscore a sobering reality: the digital ad ecosystem is inherently invasive. For the individual user, relying on the "good faith" of websites is no longer a viable strategy.
1. Browser-Level Defense
For desktop users, uBlock Origin Lite remains the gold standard. It is open-source, resource-efficient, and effective at blocking the tracking scripts that feed the data brokers identified by DecryptAds. For Firefox users, it is also effective on mobile platforms.

2. The Network Perimeter (The "Gold Standard")
For those who want to secure every device in their home—including smart TVs and IoT devices—a hardware-based approach is best. Installing Pi-hole on a Raspberry Pi acts as a network-wide DNS sinkhole. By redirecting ad-serving requests to a "null" destination, you prevent ads from ever reaching your devices.
3. App Skepticism
The most dangerous frontier is the mobile app. Many apps exist primarily as data-harvesting containers. When possible, favor mobile websites over dedicated apps. If you must use an app, assume it is collecting more data than you are comfortable with.
Conclusion: A New Era of Visibility
The launch of DecryptAds represents a shift in the balance of power. By transforming arcane, technical disclosures into actionable intelligence, it empowers users and researchers to see through the veneer of modern web browsing. Whether it is exposing links to sanctioned banks or tracking the proliferation of malicious AI-generated sites, the tool provides the evidence needed to demand higher standards from the digital advertising industry.
As we move forward, the question for regulators and tech giants alike is no longer what data is being collected, but who is allowed to access it—and at what cost to our collective security. Through the lens of DecryptAds, the answer is finally coming into focus.


 Ali Ikhwan
 Basiran





