
 Muslim
In a stunning turn of events that has sent shockwaves through the cybersecurity industry, federal agents have arrested a prominent Canadian security expert on charges related to the notorious "ShinyHunters" hacking syndicate. The arrest, which took place in Pennsylvania this week, marks a significant escalation in the FBI’s pursuit of the group—a collective that recently managed the unthinkable: infiltrating the Bureau itself and exfiltrating sensitive data concerning thousands of federal agents.
While the FBI has remained tight-lipped regarding the specific identity of the individual, sources close to the investigation have confirmed to KrebsOnSecurity that the detainee is a co-founder of a Canadian cybersecurity firm. The individual, identified through court records as Edward Dubrovsky (appearing in some filings as "Dobrovsky"), was apprehended while attending the Cyber Risk Summit in Philadelphia, an industry gathering focused on the volatile world of cyber insurance and ransom negotiations.
The Intersection of Ransomware and Law Enforcement
The arrest of Mr. Dubrovsky highlights a burgeoning, and increasingly murky, sector of the tech economy: the professionalization of ransomware negotiation. Many cybersecurity firms now offer services to corporations that have been hit by ransomware, acting as intermediaries between the victims and the criminal gangs holding their data hostage.
However, the line between "negotiator" and "co-conspirator" is now under intense federal scrutiny. Investigators are probing whether some of these intermediaries are doing more than simply facilitating payments. In the case of the ShinyHunters—a group that has extorted over $70 million from victims this year alone—the FBI is investigating whether certain "security experts" provided the strategic guidance necessary for the hackers to maximize their leverage.
The charges filed against Dubrovsky include "conspiracy to threaten to impair the confidentiality of information with the intent to extort money" and "interference with commerce by threats." These charges suggest that the government believes the defendant was not merely a passive negotiator, but an active participant in the coercive process.
Chronology of a High-Stakes Investigation
The trajectory of this investigation has moved with unprecedented speed, particularly following the brazen theft of FBI internal data.

- September 2026: Dutch authorities, working in coordination with international partners, arrest Pepijn van der Stap, a convicted cybercriminal linked to the ShinyHunters. The seizure of his devices provided the FBI with a treasure trove of intelligence, including encrypted communications that allegedly implicated various intermediaries.
- Late September 2026: Following Van der Stap’s arrest, a secondary figure known as "Rey" assumes control of ShinyHunters. In an act of extreme provocation, Rey publishes sensitive data stolen from an FBI recruitment portal, including medical and psychiatric records of agents.
- October 5–7, 2026: The Cyber Risk Summit is held at the Loews Philadelphia Hotel. Dubrovsky, a noted author on the subject of cyber extortion, is in attendance as a representative of his firm, CyberSteward.
- October 7, 2026: Reports emerge that "Rey"—identified as Jordanian teenager Saif Al-din Khader—has been detained by Jordanian authorities and is cooperating with investigators.
- October 8, 2026: Edward Dubrovsky is arrested in Pennsylvania.
- October 9, 2026: Court records indicate that the case has been transferred to the Eastern District of Texas, which has been centralized as the hub for all ShinyHunters-related prosecutions.
The "Negotiator’s" Dilemma: A Philosophical Pivot
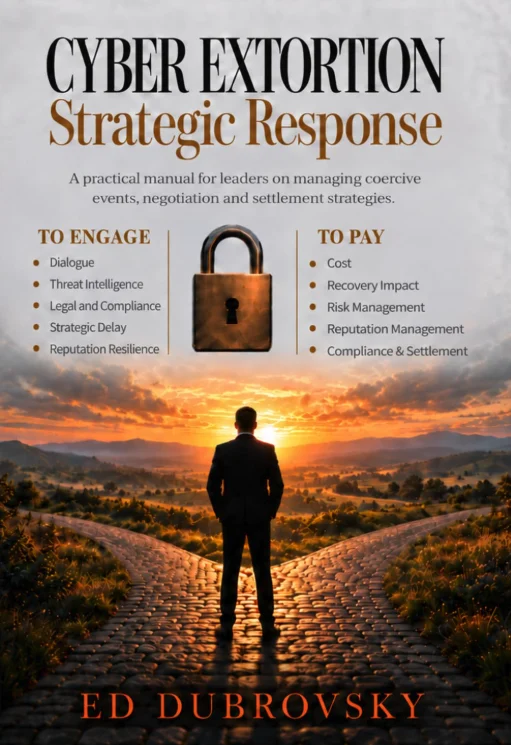
The irony of the arrest is underscored by Dubrovsky’s own published work. As the author of Cyber Extortion Strategic Response, a 252-page manual, Dubrovsky positioned himself as a thought leader on how organizations should handle digital blackmail.
In his writing, Dubrovsky emphasized that "communicating with a criminal is not the same as negotiating a payment." He argued that engagement is a vital tool for gathering information, stalling for time, and preserving options. However, federal prosecutors now appear to be testing the limits of that philosophy. The government’s central question seems to be: at what point does "gathering information" and "negotiating a settlement" cross the legal threshold into aiding and abetting a criminal conspiracy?
By his own admission in recent professional posts, Dubrovsky advocated for "strategy & compliant driven coercive advisory." To the FBI, however, the word "coercive" in the context of an outside actor may be the smoking gun that links his consulting services to the illegal activities of the ShinyHunters.
Official Responses and Procedural Status
The FBI has maintained a wall of silence regarding the specifics of the case. FBI Director Kash Patel, who previously confirmed the arrest via social media, has not provided further details on how the Bureau intends to handle the potential conflict of interest arising from the fact that its own internal data was compromised by the very group the defendant is accused of assisting.
Currently, Dubrovsky is being held in a federal facility in Philadelphia, though his case is in the process of being transferred to the Eastern District of Texas. Notably, court records indicate that he does not yet have legal counsel, and the court has not officially appointed a public defender. This lack of representation, coupled with the fact that several core documents in the complaint remain under seal, suggests that the government is in the early stages of a much broader crackdown.
Implications for the Cybersecurity Industry
The arrest has sent a chill through the cyber insurance and incident response communities. Many firms that provide negotiation services are now reviewing their internal protocols to ensure their compliance with federal anti-extortion laws.

The industry’s reliance on the "gray market" of ransomware negotiations is now under a microscope. If the FBI succeeds in proving that high-level consultants were facilitating the criminal goals of groups like ShinyHunters, the entire business model of "ransomware recovery" could face a massive regulatory overhaul.
Furthermore, the compromise of the FBI’s own data remains a haunting backdrop to this story. The fact that an adversary could not only steal but also weaponize the personal data of the very agents tasked with hunting them down has humiliated the Bureau. The drive to secure a conviction in the Dubrovsky case is likely fueled by a desire to restore the agency’s reputation and demonstrate that no one—not even those who claim to be part of the solution—is above the law.
Looking Ahead: The Scope of the Crackdown
Sources suggest that the arrest of Dubrovsky is not an isolated incident but the beginning of a larger strategy. The FBI’s focus on the Eastern District of Texas signals that prosecutors are building a RICO-style case that could eventually ensnare other principals at security firms who may have operated with similar, questionable tactics.
As the legal proceedings shift to Texas, the cybersecurity world will be watching closely. The outcome of the case against Dubrovsky will likely set a legal precedent for how much "negotiation" is permitted before it is classified as "conspiracy." For now, the arrest serves as a stern warning: in the high-stakes game of digital extortion, the line between the hunter and the hunted has never been thinner.
This is a developing story. Further updates regarding court filings and statements from the defendant’s future legal team will be provided as they become available.


 Ali Ikhwan
 Basiran





